VTP Altitude, Wakad, Pune, Maharashtra 411033, India
VTP Altitude, Wakad, Pune, Maharashtra 411033, India
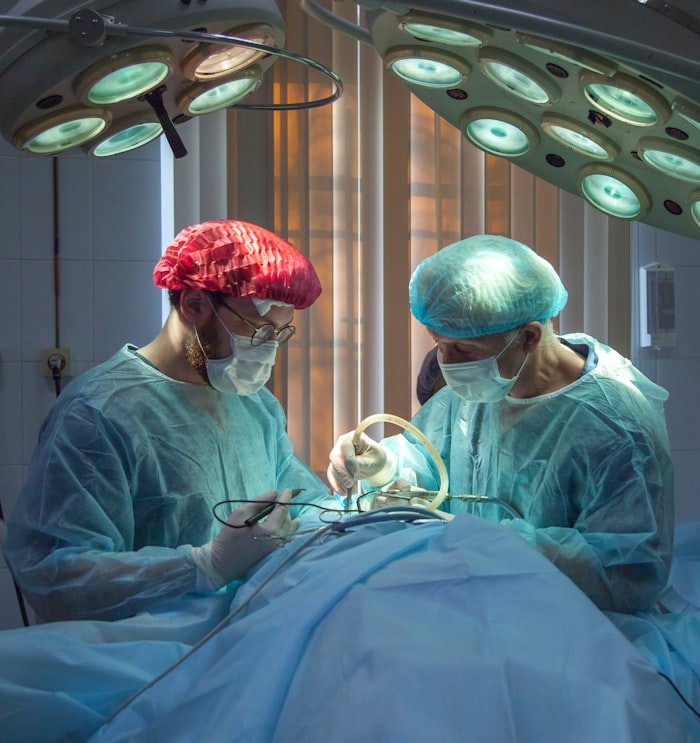
FinixSoft builds patient portals, scheduling systems and clinical records platforms designed around HIPAA-grade data handling from day one. We treat compliance as part of the architecture, not a checklist bolted on before launch.
Every healthcare engagement starts with a data-flow audit — who touches PHI, where it's stored, and how it's encrypted in transit and at rest — before a line of application code gets written.
From patient-facing scheduling tools to internal records systems your clinical staff can actually navigate, we hand off software your team can maintain without needing us on call for every change.
Compliance is designed in from the first data model, not retrofitted after an audit finding.
Role-based access controls and audit logs so you can prove who saw what, when.
Video visits and remote monitoring built to the same compliance bar as in-person care.
PHI encrypted in transit and at rest, with keys your team controls.
Every access to patient records is logged and reportable on demand.
Working with a team that's shipped HIPAA-grade systems before means fewer compliance surprises during your next audit.
Fixed-scope pricing agreed before work begins
HIPAA risk assessment included in every engagement
Full documentation and access controls handed over at project close
Yes. We sign a BAA before any engagement that touches protected health information, and we structure the system architecture around it from day one.
In most cases, yes. We commonly build integrations and custom tooling around existing EHR platforms rather than replacing them outright.
We use de-identified or synthetic data in every non-production environment, so real patient records are never exposed to a test or staging system.
We agree on scope, timeline and a fixed price before work begins, based on your EHR integrations, compliance scope and clinician workflows, so there are no surprises halfway through.
Yes. The same engineers who built your system stay on for monitoring, patching and support, with coverage in place ahead of every compliance audit.
HIPAA-compliant deployments
Every system built with a signed BAA and audited access controls.
Fewer missed appointments
After patient portal and reminder workflow improvements.
System uptime
Uptime on clinical systems, monitored around the clock.
Healthcare systems shipped
Across clinics, hospitals and telehealth providers.
1. Discover & Scope
We map your EHR/EMR integrations, compliance requirements and clinician workflows before a line of code gets written.
2. Architect
HIPAA-first data access and audit logging get designed in from the start, not bolted on before launch.
3. Build in Sprints
Senior engineers ship in short, demoable sprints so your clinical and IT teams see real progress every week.
4. Test & Harden
Security testing and a compliance review happen against real audit checklists before anything reaches production.
5. Launch & Support
We deploy, document and stay on for support — the same engineers who built it, not a new team.
Tell us what you're building — we'll reply with next steps within one business day.
Get in touchYears of experience
Building and supporting business-critical software.
Projects delivered
Across web, mobile, cloud and data platforms.
Client retention
Most clients stay on for ongoing support and new work.
Specialists on staff
Engineers, designers and analysts under one roof.