VTP Altitude, Wakad, Pune, Maharashtra 411033, India
VTP Altitude, Wakad, Pune, Maharashtra 411033, India
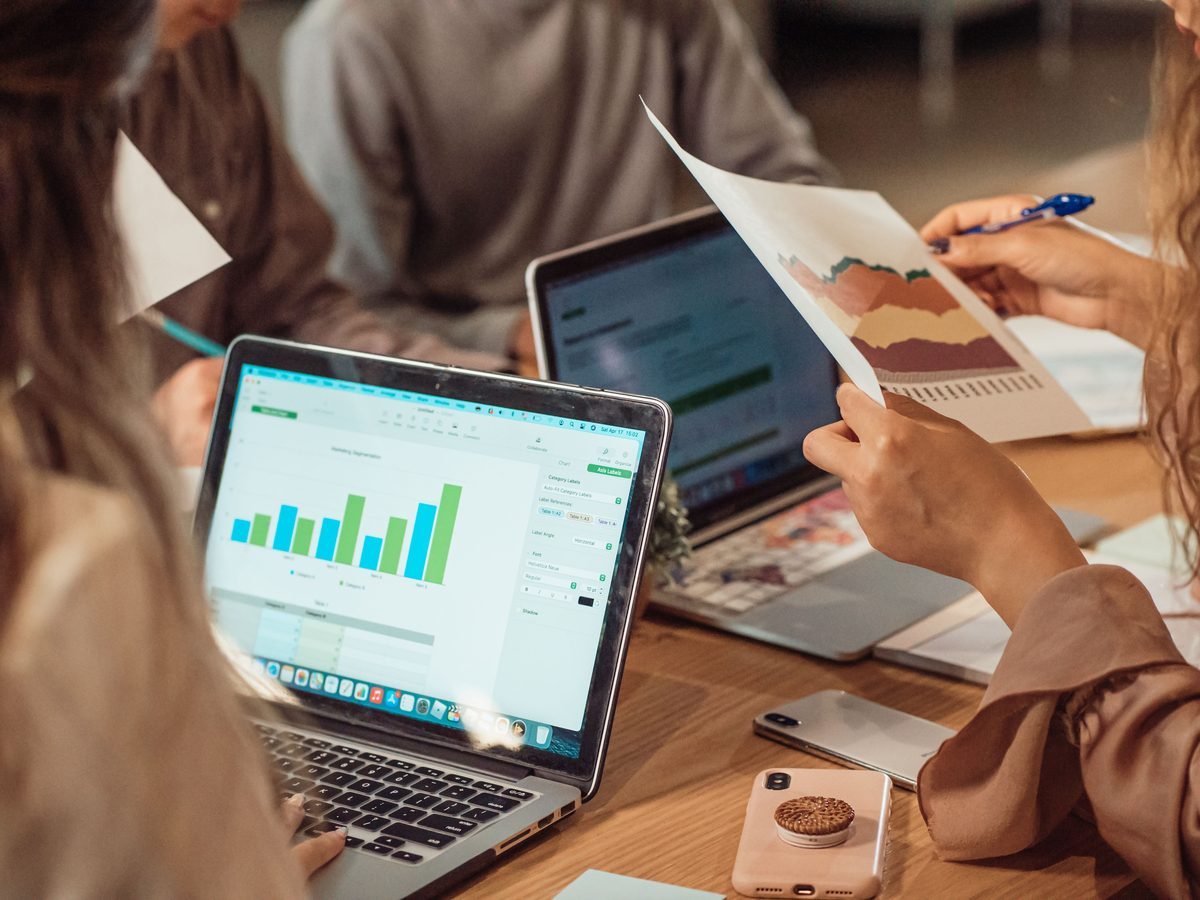
We build transaction systems, fraud-detection checks and reporting pipelines designed to hold up under a real audit, not just a product demo. Every system we ship for financial services clients is built with SOC 2 and PCI DSS requirements as first-class constraints.
Financial software fails quietly until it doesn't — a reconciliation bug or a missed fraud signal can cost real money. We build in redundancy, logging and reconciliation checks from the start, not after the first incident.
Whether it's a customer-facing banking portal or an internal reporting pipeline, we hand off systems your compliance and finance teams can audit independently, with documentation that holds up under regulatory scrutiny.
Card data handling designed to meet PCI DSS requirements from the first architecture review.
Transaction monitoring and anomaly checks designed around your actual risk model.
Every transaction is traceable, with logs your compliance team can pull on demand.
Connects cleanly to the core banking and payment rails you already run, no forced platform switch.
Systems designed around the controls your SOC 2 audit will actually test.
Automated checks that catch discrepancies before they reach a statement.
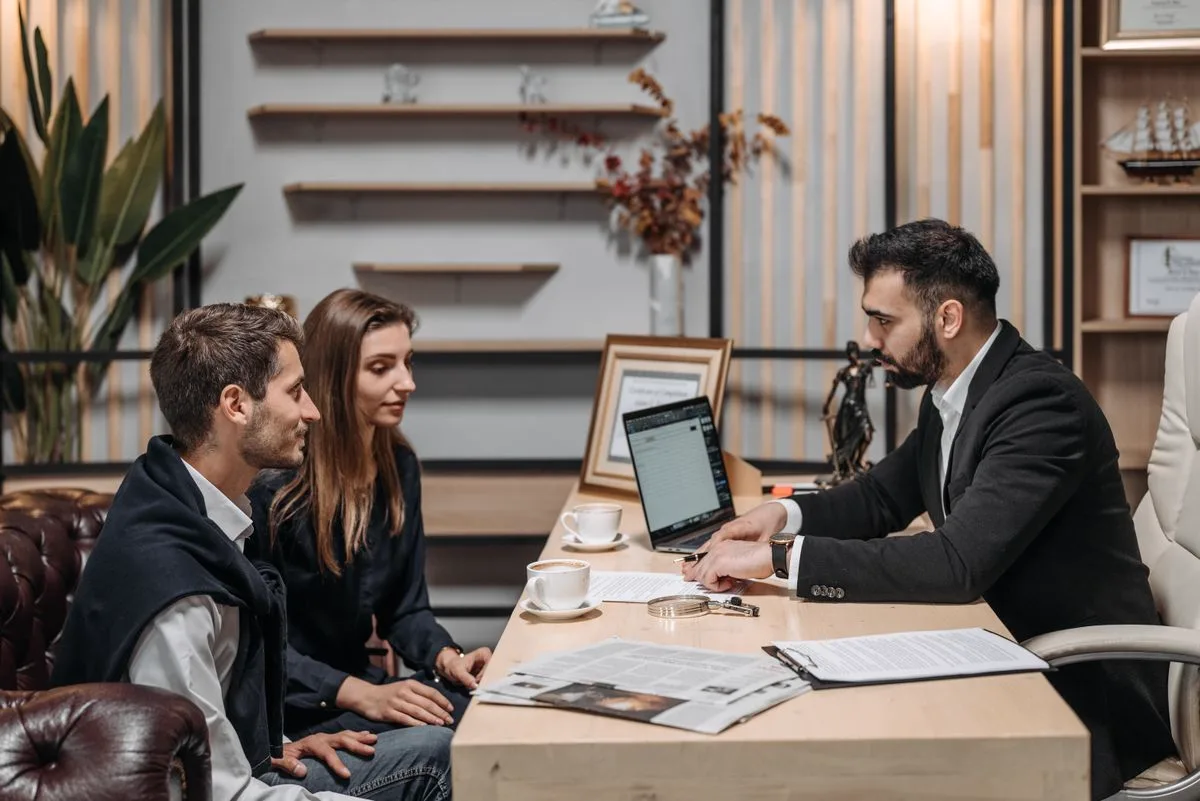
Financial services clients stay with us because the systems we build keep passing their audits, year after year.
Fixed-scope pricing agreed before work begins
Compliance review built into every milestone, not just at launch
Full documentation handed over for your audit trail
Yes, we've built transaction and reporting systems for banking and fintech clients that needed to pass SOC 2 and PCI DSS audits, not just launch a product.
Yes. We regularly integrate with existing payment processors, core banking platforms and reporting tools rather than replacing them wholesale.
We use tokenized or synthetic transaction data in every non-production environment, so live account and card data never touches a test system.
We agree on scope, timeline and a fixed price before work begins, based on your compliance requirements, integrations and audit scope, so there are no surprises halfway through.
Yes. The same engineers who built your system stay on for monitoring, patching and support, including coverage ahead of major audits or regulatory deadlines.
Audits passed on first review
Systems built to PCI DSS and regulatory standards from day one.
Uptime on core banking systems
Load-tested infrastructure that holds up under transaction volume.
Fewer fraud false-positives
After tuning detection rules on recent engagements.
Financial systems shipped
Across banking, lending, payments and insurance clients.
1. Discover & Scope
We map your compliance requirements, existing core systems and integrations before a line of code gets written.
2. Architect
Data security, audit logging and fraud controls get designed in from the start, not bolted on before launch.
3. Build in Sprints
Senior engineers ship in short, demoable sprints so your compliance and risk teams see progress every week.
4. Audit & Harden
We run security testing and a compliance review against real regulatory checklists before anything reaches production.
5. Launch & Support
We deploy, support your next audit cycle, and stay on — the same engineers who built it, not a new team.
Tell us what you're building — we'll reply with next steps within one business day.
Get in touchYears of experience
Building and supporting business-critical software.
Projects delivered
Across web, mobile, cloud and data platforms.
Client retention
Most clients stay on for ongoing support and new work.
Specialists on staff
Engineers, designers and analysts under one roof.